
PECB ISO-IEC-27001-Lead-Auditor日本語 : PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版)

- Exam Code: ISO-IEC-27001-Lead-Auditor日本語
- Exam Name: PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版)
- Updated: Oct 14, 2026
- Q & A: 418 Questions and Answers
About PECB ISO-IEC-27001-Lead-Auditor日本語 Exam
Privacy and security
As a reliable platform, we always put our customer's interests in the first place. We are deeply concerned about your privacy and security. First, our ISO-IEC-27001-Lead-Auditor日本語 test engine is safety and virus-free, thus you can rest assured to install PECB ISO-IEC-27001-Lead-Auditor日本語 real practice torrent on your computer or other electronic device. Besides, we keep our customers' financial data and personal information private and secure, and never share it with the third part without the permission of you. You can search information about the ISO-IEC-27001-Lead-Auditor日本語 PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) pdf study guide as you like. We will try our best to offer the desired material for you.
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
ISO-IEC-27001-Lead-Auditor日本語 free practice torrent
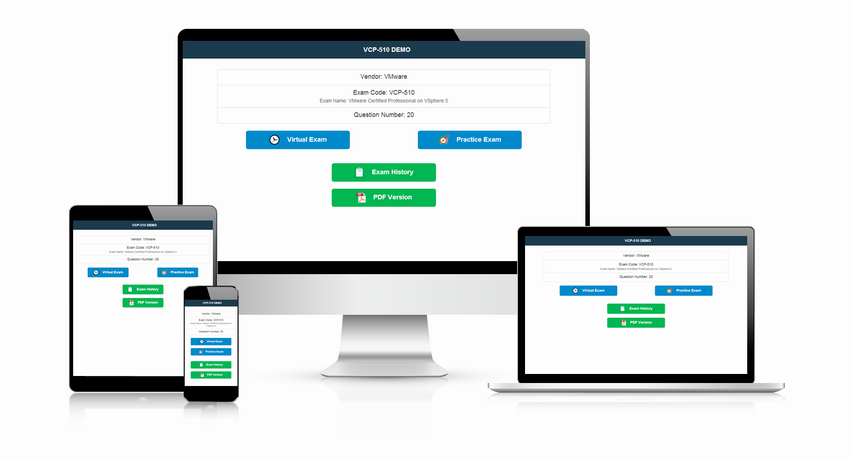
Our ISO-IEC-27001-Lead-Auditor日本語 free practice torrent is available for all of you. Simply download ISO-IEC-27001-Lead-Auditor日本語 free pdf demo and get the practice questions. The demo questions are part of the complete dumps. With our ISO-IEC-27001-Lead-Auditor日本語 free download dumps you can determine whether the ISO-IEC-27001-Lead-Auditor日本語 real questions & answers are worth your time and investment or not. The ISO-IEC-27001-Lead-Auditor日本語 free pdf demo support to be printed, while if you want the ISO-IEC-27001-Lead-Auditor日本語 test simulator for reference, we can provide you the screenshot about the practice format. If you buy the dumps from other vendors and get the unhappy result, and want to make sure the validity of our ISO 27001 ISO-IEC-27001-Lead-Auditor日本語 exam vce torrent, you can send your dumps to us, then we can check and compare them and tell you our dumps is worthy buying or not.
As an aspiring IT candidate, you are must desperate to want to pass ISO-IEC-27001-Lead-Auditor日本語 exam certification under all costs and conditions. While, our ISO-IEC-27001-Lead-Auditor日本語 free practice torrent will not only help you pass your exam, but also save your time and energy at the same time. ISO 27001 ISO-IEC-27001-Lead-Auditor日本語 sure pass torrent is the latest and edited and checked by our professional experts, which always can cover all the topics in the actual test. With our ISO-IEC-27001-Lead-Auditor日本語 exam vce torrent, you will test your knowledge and skills, and know more about the actual test. You will not waste much time on several times for test. One time pass with PECB ISO-IEC-27001-Lead-Auditor日本語 free download dumps is the guarantee for all of you.

PECB ISO-IEC-27001-Lead-Auditor日本語 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
Reference: https://pecb.com/pdf/candidate-handbooks/pecb-candidate-handbook-iso-27001-lead-auditor-mc.pdf
ISO-IEC-27001-Lead-Auditor日本語 test engine for sure pass
The ISO-IEC-27001-Lead-Auditor日本語 test engine provides you with a virtual examination environment, which further helps you to be more familiar with the ISO-IEC-27001-Lead-Auditor日本語 actual test. The ISO-IEC-27001-Lead-Auditor日本語 test engine comes with many features which save your time for other training classes. With the ISO-IEC-27001-Lead-Auditor日本語 real questions & answers, you will easily memorizing the important concepts, and will feel as you are in the actual test. It is very good to experience the simulate environment in advance. Besides, at the end of each test the result will be declared along with the mistakes, so that you can know your weakness and strengthen about ISO-IEC-27001-Lead-Auditor日本語 PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) actual test, then make the detail study plan for further learning. In addition, when you receive our ISO-IEC-27001-Lead-Auditor日本語 exam vce torrent, you can download it with the computer, and then install it on your phone or other device. It is very convenient to study with our ISO-IEC-27001-Lead-Auditor日本語 sure pass torrent.
PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor日本語版) Sample Questions:
シナリオ7
Lawsyは、タイのバンコクにオフィスを構える大手法律事務所です。50名以上の弁護士が、ビジネス法、商法、知的財産、銀行、金融サービスなど、幅広い分野で高度な法的サービスをクライアントに提供しています。
彼らは、情報セキュリティのベストプラクティスを実践し、技術開発の最新情報を常に把握することに尽力してきたおかげで、市場において確固たる地位を築いていると確信している。
Lawsy社は、情報セキュリティマネジメントシステム(ISMS)に関して、2年間にわたり厳格な導入、評価、内部監査を実施してきました。そして今回、知名度が高く信頼できる認証機関であるISMAに対し、ISO/IEC 27001認証の申請を行いました。
第1段階の監査において、監査チームは導入段階で作成されたすべてのISMS文書をレビューしました。また、経営陣によるレビューおよび内部監査の記録もレビューし、評価しました。Lawsy社は、不適合に対する是正措置が必要に応じて実施されたことを示す証拠記録を提出したため、監査チームは内部監査担当者にインタビューを実施しました。このインタビューにより、内部監査計画および手順に関する知見が得られ、内部監査の適切性と頻度が検証されました。
監査チームは、情報セキュリティポリシーやリスク評価基準などの戦略文書の検証を継続しました。情報セキュリティポリシーのレビュー中に、チームはガバナンスフレームワークと手順を説明する文書情報の間に矛盾があることに気づきました。ステージ1の完了後、監査チームリーダーは監査の目的、範囲、基準、手順を定めた監査計画を作成しました。
第2段階の監査において、監査チームは情報セキュリティポリシーを作成した情報セキュリティマネージャーにインタビューを行った。彼は、第1段階で指摘された問題について、Lawsy社は3ヶ月ごとに義務的な情報セキュリティ研修と啓発セッションを実施していると述べて正当化した。
その後、監査チームは、従業員が職場外にノートパソコンを持ち出すことは許可されていたものの、Lawsy社には職場外でのノートパソコン使用に関する手順が定められていなかったことを発見した。同社はノートパソコンの使用に関する一般的な情報を提供するだけで、ノートパソコンに保存されている情報の機密性と完全性を保護するために、従業員の常識に頼っていた。
面接後、監査チームは従業員研修記録50件のうち15件を調査し、Lawsy社が研修および意識向上に関するISO/IEC 27001の要件を満たしていると結論付けました。この結論を裏付けるため、監査員は監査完了後、調査対象となった従業員研修記録をコピーし、保管しました。
質問
Lawsyには、職場外でのノートパソコンの使用に関する手順が定められておらず、ノートパソコンに保存されている情報の機密性を保護するために、従業員の常識に頼っている。これはどのような問題を引き起こすだろうか?
- A. 不適合
- B. 異常
- C. 適合性
Correct Answer: A 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
シナリオ3:NightCoreは、米国に拠点を置く多国籍テクノロジー企業で、電子商取引、クラウドコンピューティング、デジタルストリーミング、人工知能に重点を置いています。情報セキュリティマネジメントシステム(ISMS)を導入してから8か月以上経過した後、ISO/IEC 27001の認証を取得するために、認証機関に第三者監査の実施を依頼しました。
認証機関は7名の監査員からなるチームを編成した。その中で最も経験豊富なジャックが監査チームのリーダーに任命された。彼は長年にわたり、ISO/IEC 27001主任監査員、CISA、CISSP、CISMなど、数々の著名な資格を取得してきた。
ジャックは、NightCore が実装したすべての情報セキュリティ要件とコントロールを調査および評価することにより、ISMS 監査の各フェーズで徹底的な分析を実施しました。ステージ 2 監査中に、ジャックはいくつかの不適合を検出しました。ソフトウェア ライセンスの購入請求書の数をソフトウェア インベントリと比較した後、ジャックは、会社が多くのコンピュータでソフトウェアの違法バージョンを使用していることを発見しました。彼は、この不適合について経営陣に説明を求め、彼らがこれを認識しているかどうかを確認することにしました。彼の次のステップは、NightCore の IT 部門を監査することでした。経営陣は、NightCore のシステム管理者であるトムをガイド役として任命し、ジャックと監査チームがシステムの内部構造とデジタル資産インフラストラクチャを調査できるようにしました。
監査担当者は財務部の職員に聞き取り調査を行った際、同社が最近、コンサルタントの一人に対して異常に高額な取引を行っていたことを発見した。取引に関する必要な詳細情報をすべて収集した後、ジャックは経営陣に直接聞き取り調査を行うことにした。
最初の不適合について話し合った際、経営陣はジャックに対し、コピー版ソフトウェアの方が安価だったため、オリジナル版ではなくコピー版を使用することに意図的に決めたと説明した。ジャックはナイトコアの経営陣に対し、違法バージョンのソフトウェアを使用することはISO/IEC 27001の要件および国内法規に違反すると説明したが、彼らは特に問題視していないようだった。
監査から数か月後、ジャックは監査中に収集したナイトコアの情報の一部を、ナイトコアの競合他社に巨額の金銭で売却した。
このシナリオに基づいて、次の質問に答えてください。
監査原則に基づくと、ジャックは2つ目の不適合について認証機関に連絡すべきでしょうか?
シナリオ3を参照してください。
- A. はい、監査員はこのような状況を認証機関に報告すべきですが、経営陣には報告すべきではありません。
- B. いいえ、金融犯罪を示唆する可能性のある状況はISMS監査の焦点ではありません。
- C. はい、監査員はこのような状況について、認証機関の倫理委員会のメンバーに連絡して助言を求めるべきです。
Correct Answer: A 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
シナリオ3:Rebuildyはタイのバンコクに拠点を置く建設会社で、住宅の設計、建設、保守を専門としています。機密性の高いプロジェクトデータと顧客情報のセキュリティを確保するため、RebuildyはISO/IEC 27001に基づくISMS(情報セキュリティマネジメントシステム)を導入することを決定しました。これには、情報セキュリティリスクの包括的な理解、明確な継続的改善アプローチ、および堅牢なビジネスソリューションが含まれます。
ISMS導入の成果を以下に示します。
情報セキュリティは、一連のセキュリティ対策を適用し、ポリシー、プロセス、手順を確立することによって実現されます。
セキュリティ対策はリスク評価に基づいて実施され、リスクを排除または許容可能なレベルまで低減することを目的としています。
*すべてのプロセスは、計画・実行・評価・改善(PDCA)モデルに基づき、ISMSの継続的な改善を保証します。
情報セキュリティポリシーは、最良のセキュリティ慣行に基づいて作成されたセキュリティマニュアルの一部であるため、単独の文書ではありません。
情報セキュリティに関する役割と責任は、すべての従業員の職務記述書に明確に記載されています。
*ISMSの経営陣によるレビューは、計画された間隔で実施されます。
Rebuildy は、2 回の中間経営レビューと 1 回の年次内部監査を経て認証を申請しました。認証監査の前に、Rebuildy の元従業員の 1 人が監査チームのメンバーの 1 人に近づき、Rebuildy には会社が隠蔽しようとしているセキュリティ上の問題がいくつかあると伝えました。元従業員は文書化された証拠を監査チームのメンバーに提示しました。Rebuildy の主要顧客である Electra も同じ問題について証拠を提出し、監査人は元従業員の証拠ではなくこの証拠を採用することにしました。監査チームのメンバーは監査が完了するまで Electra と連絡を取り続け、監査中に発見された不適合について話し合いました。Electra はこれらの発見を裏付ける追加の証拠を提供しました。
監査の開始時に、監査チームは同社の経営陣にインタビューを行った。インタビューでは、経営陣のISMS導入への取り組みなどについて話し合われた。これらの話し合いから得られた証拠は書面による確認書に記録され、RebuildyがISO/IEC 27001のいくつかの条項に適合しているかどうかを判断するために使用された。Electraから得られた文書化された証拠は、不適合報告書とともに監査報告書に添付された。特に、以下の不適合が検出された。
会社の財務報告システムにおいて、不適切なユーザーアクセス制御設定が検出されました。
独立した情報セキュリティポリシーは策定されていません。代わりに、当社はセキュリティに関するベストプラクティスに基づいて作成されたセキュリティマニュアルを使用しています。
監査チームからこれらの文書を受け取った後、チームリーダーはRebuildyの経営陣と面会し、監査結果を報告した。監査チームは、財務報告システムと独立した情報セキュリティポリシーの欠如に関する調査結果を報告した。経営陣は調査結果に不満を表明し、監査チームリーダーの行動はプロ意識に欠けると示唆し、交代を要求する可能性を示唆した。プレッシャーを受けた監査チームリーダーは、検出された不適合の重要性を軽視するために経営陣と協力することにした。その結果、監査チームリーダーは報告書をより好ましい内容に修正し、Rebuildyのコンプライアンス問題の真の深刻さを誤って伝えてしまった。
上記のシナリオに基づいて、次の質問に答えてください。
質問:
監査人が、元従業員から提供された証拠よりも、エレクトラ社から提供された証拠を優先的に保管することは許容されるでしょうか?
- A. いいえ、元従業員からの証拠は顧客からの証拠よりも常に信頼性が高いからです
- B. いいえ、両方の証拠源は保持され、同等に評価されるべきです。
- C. はい、クライアントからの証拠は、クライアントが独立した立場にあるため、より信頼性が高いと考えられているからです。
Correct Answer: B 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
あなたは経験豊富なISMS監査チームリーダーで、監査チームに配属された研修中の監査員と話しています。あなたは、情報セキュリティマネジメントシステムの運用に関して、PDCAサイクルのチェック段階の重要性を研修中の監査員が理解していることを確認したいのです。
これは、彼に文を最も適切に完成させる単語を選ばせることで行います。
文を完成させるには、空欄部分をクリックして赤色にハイライト表示させ、下の選択肢から該当するテキストをクリックしてください。または、選択肢を適切な空欄部分にドラッグ&ドロップすることもできます。
Correct Answer:

Explanation:
* Review is the third stage of the Plan-Do-Check-Act (PDCA) cycle, which is a four-step model for implementing and improving an information security management system (ISMS) according to ISO
/IEC 27001:202212. Review involves assessing and measuring the performance of the ISMS against the established policies, objectives, and criteria12.
* Assess is the verb that describes the action of reviewing the ISMS. Assess means to evaluate, analyze, or measure something in a systematic and objective manner3. Assessing the ISMS involves collecting and verifying audit evidence, identifying strengths and weaknesses, and determining the degree of conformity or nonconformity12.
* Regular is the adjective that describes the frequency or interval of reviewing the ISMS. Regular means occurring or done at fixed or uniform intervals4. Reviewing the ISMS at regular intervals means conducting internal audits and management reviews periodically, such as annually, quarterly, or monthly, depending on the needs and risks of the organization12.
* Suitability is one of the attributes that describes the quality or outcome of reviewing the ISMS. Suitability means being appropriate or fitting for a particular purpose, person, or situation5. Reviewing the ISMS for suitability means ensuring that it is aligned with the organization's strategic direction, business objectives, and information security requirements12.
References :=
* ISO/IEC 27001:2022 Information technology - Security techniques - Information security management systems - Requirements
* ISO/IEC 27003:2022 Information technology - Security techniques - Information security management systems - Guidance
* Assess | Definition of Assess by Merriam-Webster
* Regular | Definition of Regular by Merriam-Webster
* Suitability | Definition of Suitability by Merriam-Webster
質問
監査範囲と監査基準は誰が設定するのか?
- A. 監査チームは被監査者と協議した後
- B. 認証機関
- C. 監査チームリーダー
Correct Answer: B 🗳️
Explanation: Only visible for Free4Torrent members. You can sign-up / login (it's free).
Viewing page 1 out of 84 pages.
Viewing questions 1-5 out of 418 questions.
Related Exam
- ISO-IEC-27001-Lead-Implementer-German pdf dumps torrent
- ISO-IEC-27001-Lead-Auditor pdf dumps torrent
- ISO-IEC-27001-Lead-Auditor-CN pdf dumps torrent
- ISO-IEC-27001-Lead-Auditor-Deutsch pdf dumps torrent
- ISO-IEC-27001-Lead-Auditor-KR pdf dumps torrent
- ISO-IEC-27001-Lead-Implementer pdf dumps torrent
- ISO-IEC-27035-Lead-Incident-Manager pdf dumps torrent
- ISO-IEC-27001-Lead-Auditor-JPN pdf dumps torrent
Related Certifications
Over 62957+ Satisfied Customers
 0 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
Quality and Value
Free4Torrent Practice Exams are written to the highest standards of technical accuracy, using only certified subject matter experts and published authors for development - no all study materials.
Tested and Approved
We are committed to the process of vendor and third party approvals. We believe professionals and executives alike deserve the confidence of quality coverage these authorizations provide.
Easy to Pass
If you prepare for the exams using our Free4Torrent testing engine, It is easy to succeed for all certifications in the first attempt. You don't have to deal with all dumps or any free torrent / rapidshare all stuff.
Try Before Buy
Free4Torrent offers free demo of each product. You can check out the interface, question quality and usability of our practice exams before you decide to buy.

The latest & valid real study questions with the verified answers can ensure you pass your actual test at first try. Download the free study torrent for your exam preparation and start study immediately. You will success with ease by our real questions.